News & Events

News

Latest industry updates, including news and PCI-related knowledge.

Article cover
pci-dss-vulnerability-scan-vs-penetration-test
September 14, 2026

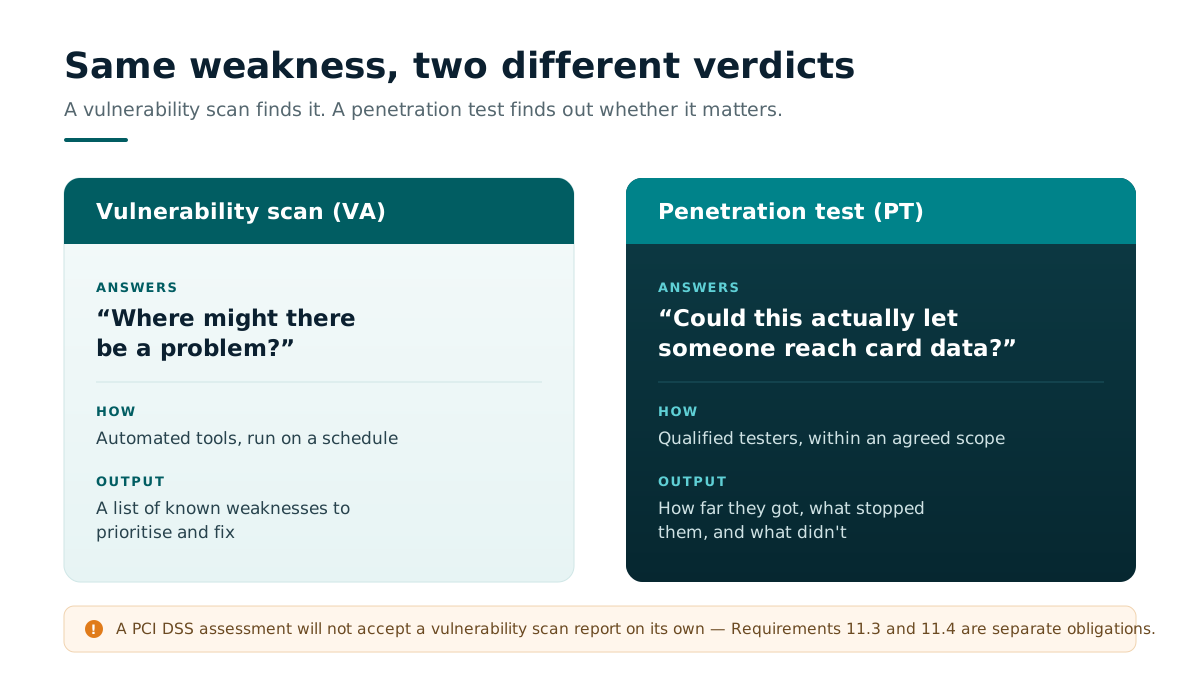
A Vulnerability Scan Is Not a Penetration Test: A PCI DSS Merchant's Guide

What's the difference between a vulnerability scan and a penetration test? A clear breakdown of PCI DSS Requirements 11.3 and 11.4 — testing frequency, internal vs. external scope, and how to spot a real penetration test report.

Read article →
Article cover
cra-standards-gap-analysis
September 12, 2026

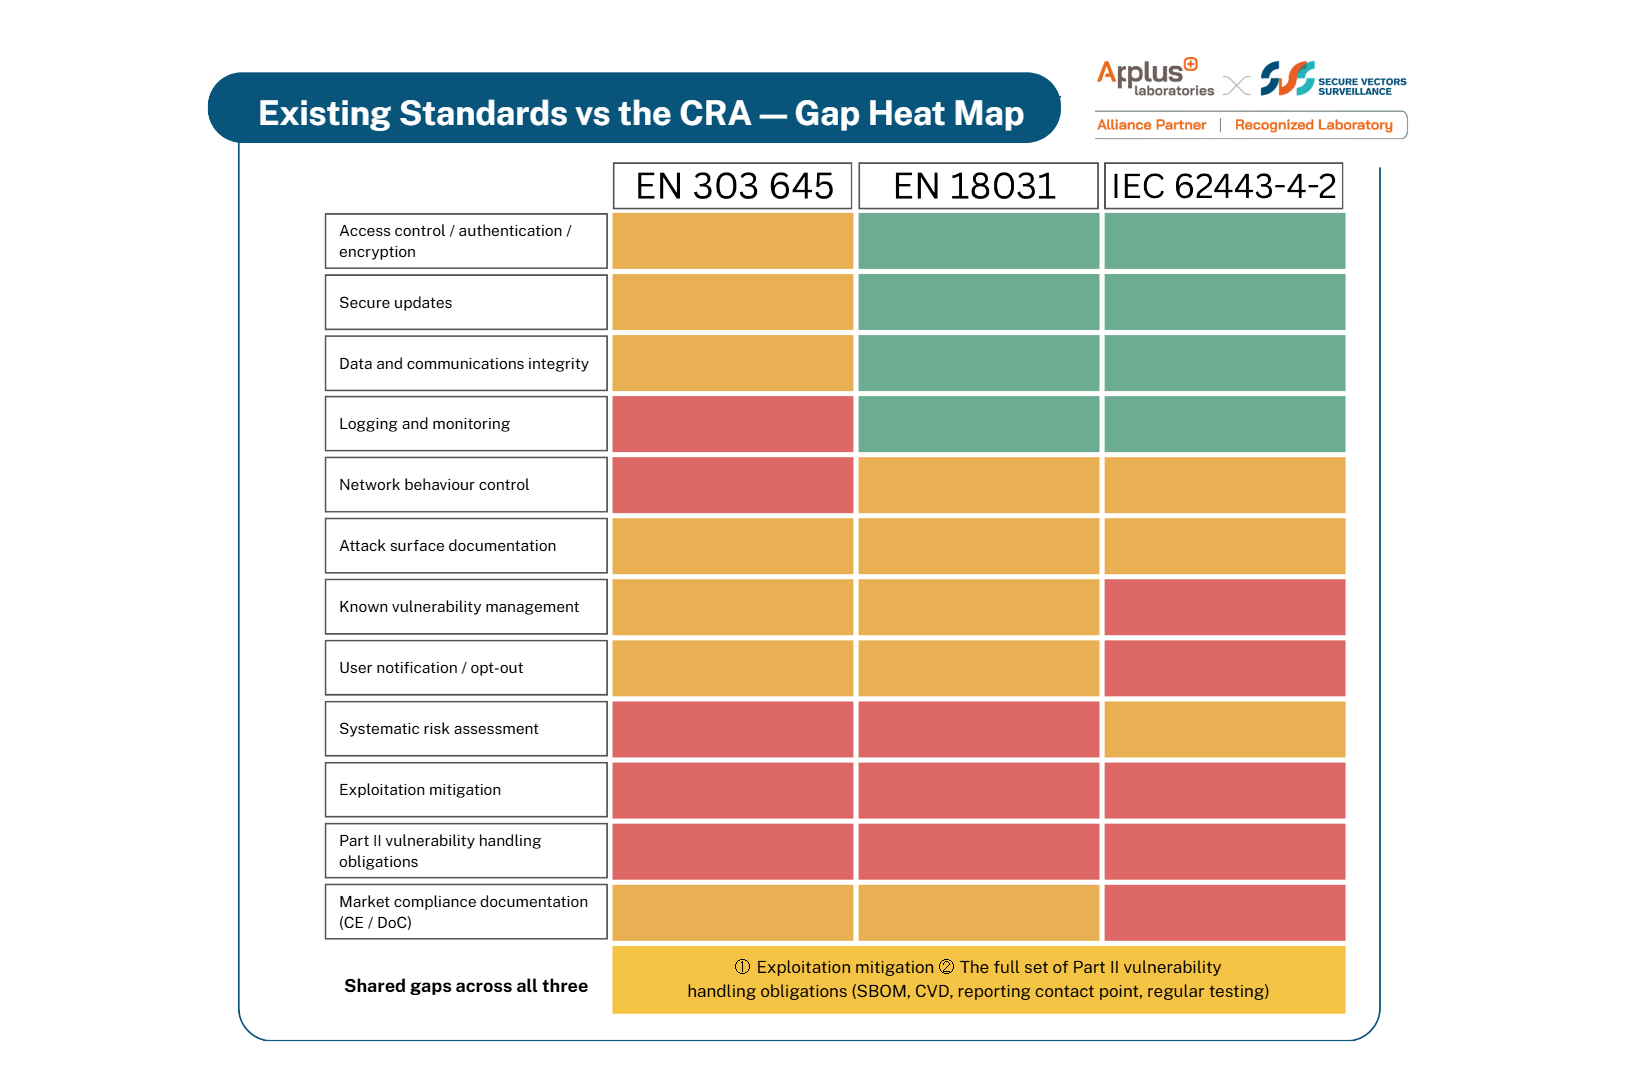
No Need to Wait for EN 40000-1-4: Start Preparing for the CRA with the Standards You Already Have

The prEN 40000 harmonised standards matched to the CRA are still in draft, but manufacturers need not wait. From a laboratory's point of view, this article analyses how far EN 303 645, EN 18031 and IEC 62443-4-2 each carry you, what is still missing, and the two gaps every manufacturer shares.

Read article →
https://securevectorlab.com/news/cra-standards-gap-analysis
Article cover
cra-conformity-assessment-modules
September 11, 2026

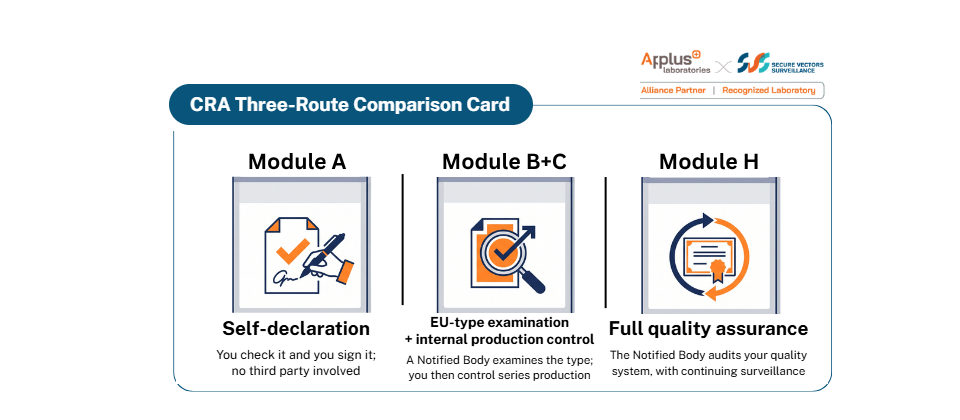
How Does CRA Conformity Assessment Work? Comparing Modules A, B+C and H

Once the classification is settled, how do you choose a CRA conformity assessment route? Using a router, a firewall and a smart doorbell, this article unpacks the differences between Modules A, B+C and H, the documentation each requires, and where the notified body queue stands in 2026.

Read article →
https://securevectorlab.com/news/cra-conformity-assessment-modules
Article cover
cra-class-i-class-ii
September 10, 2026

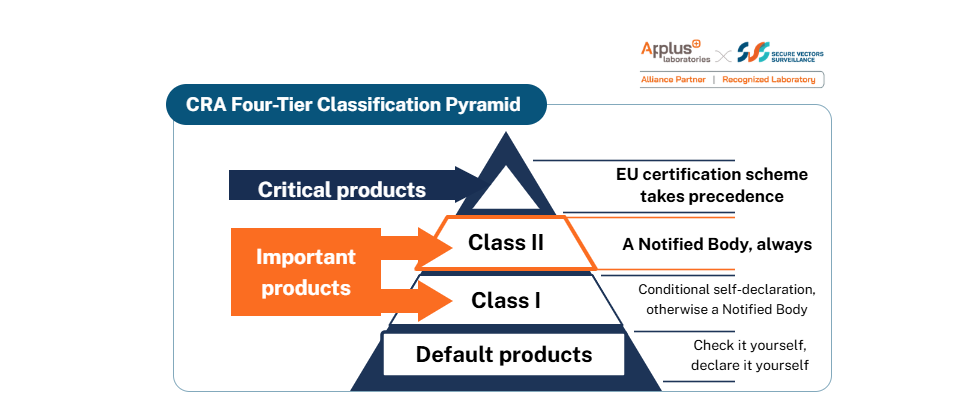
Is My Product Class I or Class II? CRA Product Classification, Explained Through One Router

How is CRA product classification determined? Using a router, a firewall and a smart doorbell, this article unpacks the difference between default products and important products Class I / Class II, how to make the call, and where the rules stand in 2026 — so manufacturers can pin down their own obligations.

Read article →
https://securevectorlab.com/news/cra-class-i-class-ii
Article cover
cra-sbom-part-2
September 2, 2026

SBOM Part 2 | How Far Does the CRA's SBOM Requirement Actually Go?

The SBOM associated with EN 18031 certification is not quite the SBOM the CRA requires. Starting from the CRA text, this article explains the SBOM's legal position, the itemised requirements in the draft prEN 40000 harmonised standards, and how it connects to penalties and reporting obligations.

Read article →
https://securevectorlab.com/news/cra-sbom-part-2
Article cover
cra-sbom-part-1
September 1, 2026

SBOM Part 1 | What Is an SBOM? And Why Is Every Customer Suddenly Asking for One?

More and more customers are demanding an SBOM in contracts and security questionnaires. This article uses everyday analogies to explain what an SBOM is, why almost every customer is asking for one now, and what a genuinely usable SBOM has to contain.

Read article →
https://securevectorlab.com/news/cra-sbom-part-1
Article cover
cra-annex-i-requirements
August 31, 2026

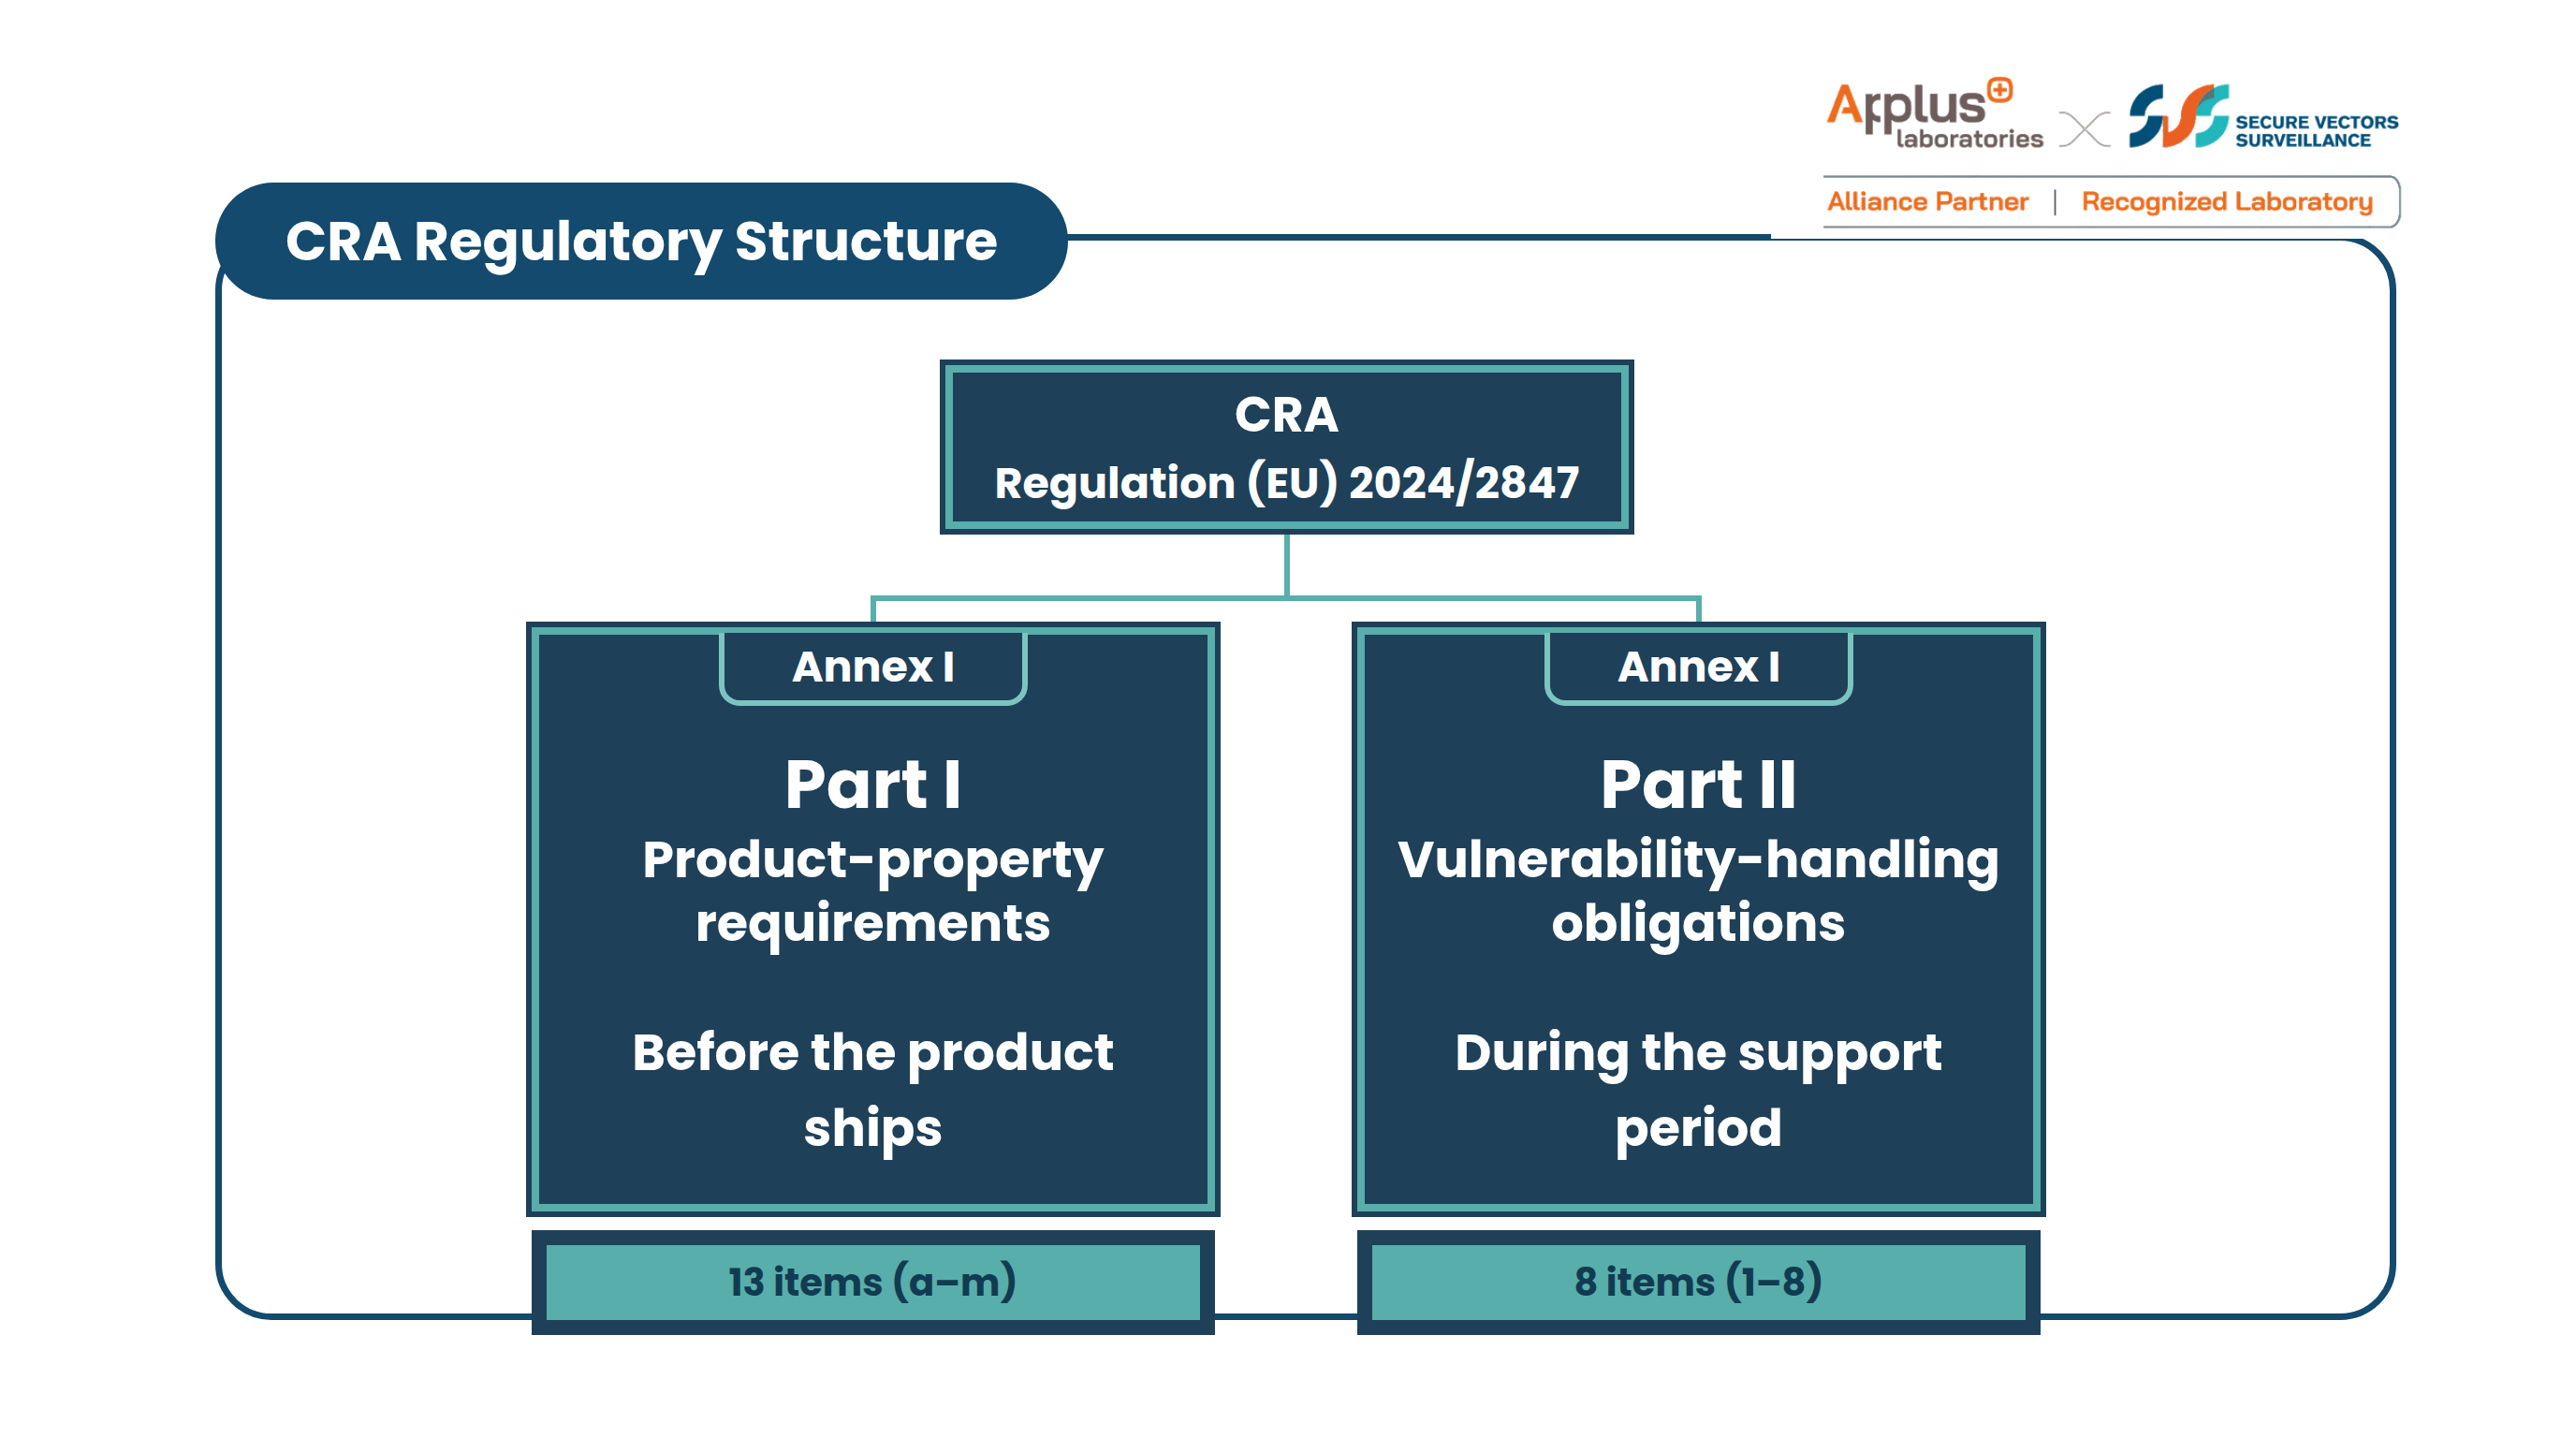
Breaking Down CRA Annex I: 13 Product Requirements + 8 Vulnerability-Handling Obligations

Annex I is the only part of the CRA that directly specifies what the product must do — the compliance backbone that technical documentation, CE marking and the penalty regime all point to. A testing-laboratory breakdown of Part I's 13 product requirements and Part II's 8 vulnerability-handling obligations.

Read article →
https://securevectorlab.com/news/cra-annex-i-requirements
Article cover
cra-article-14-internal-sop
August 25, 2026

Part 2 | The Rules Are the Easy Part: Building the Internal SOP for CRA Article 14

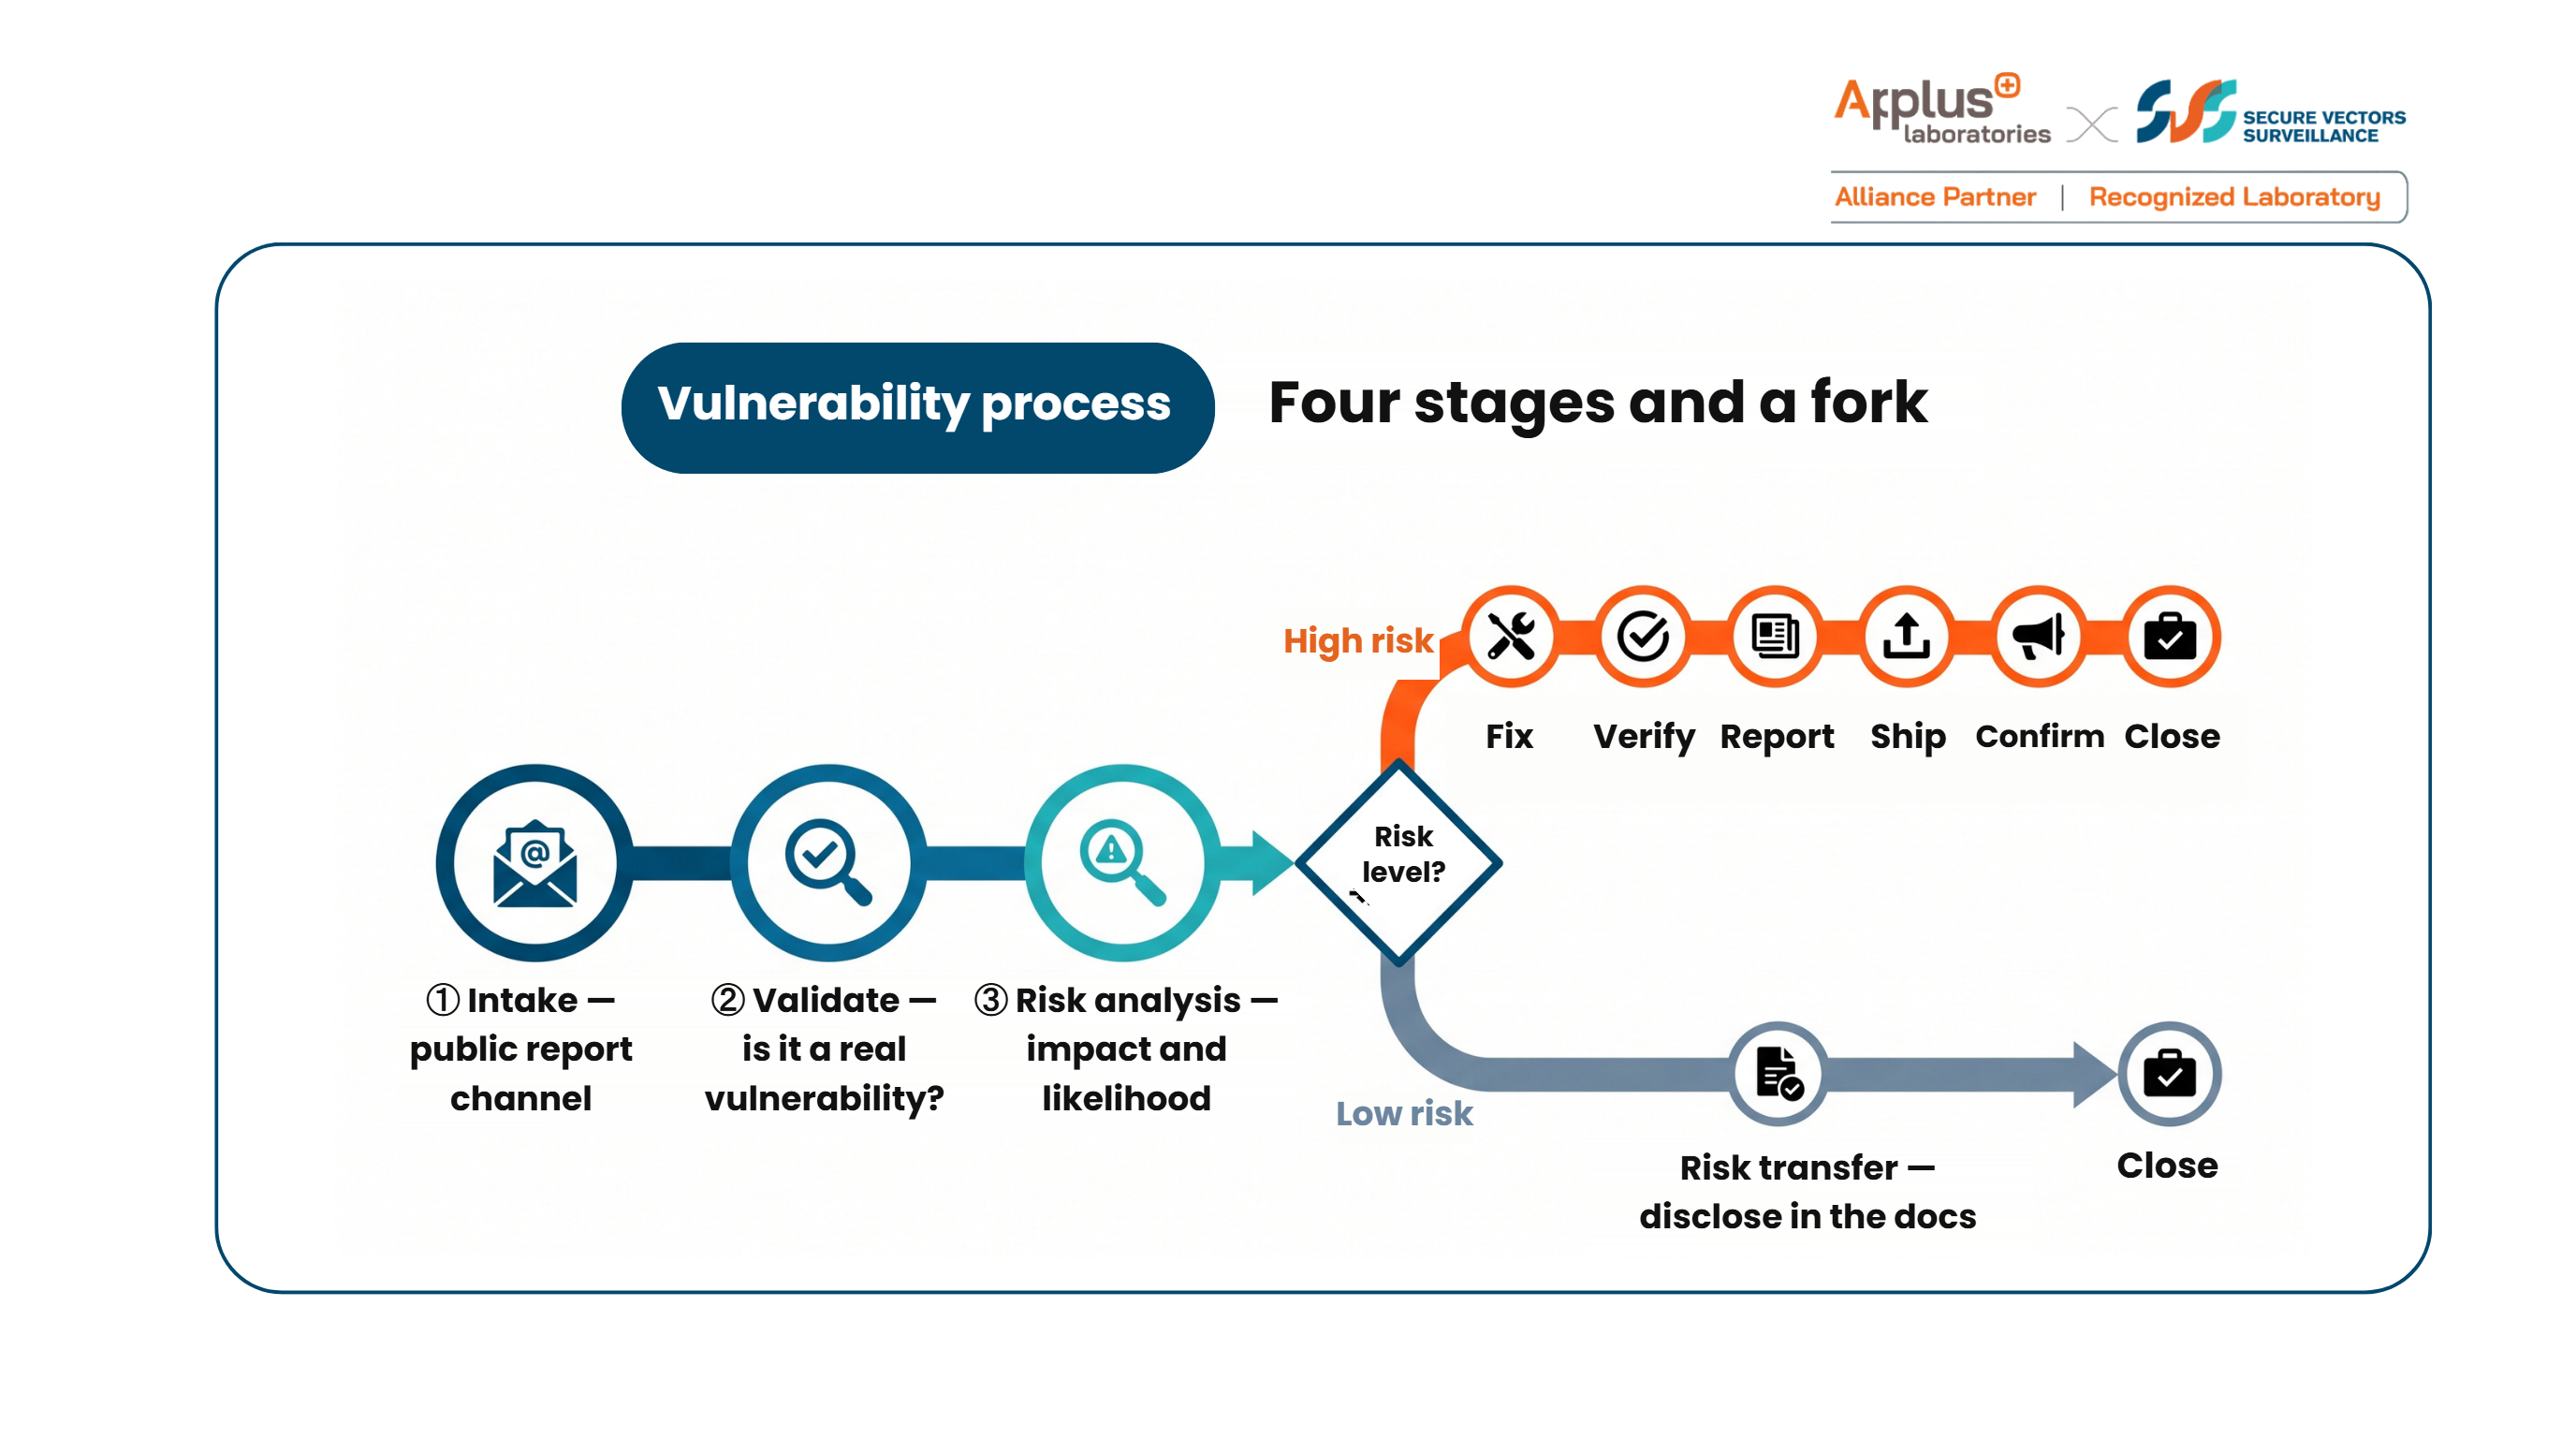
The 24-hour and 72-hour reporting deadlines in Article 14 of the EU Cyber Resilience Act (CRA) test whether a company has a process that can actually carry them. This article breaks down the skeleton of an internal vulnerability management SOP, the split between reporting to the authorities and notifying customers, and several blind spots we see repeatedly among manufacturers.

Read article →
https://securevectorlab.com/news/cra-article-14-internal-sop
Article cover
cra-article-14-reporting-obligations
August 24, 2026

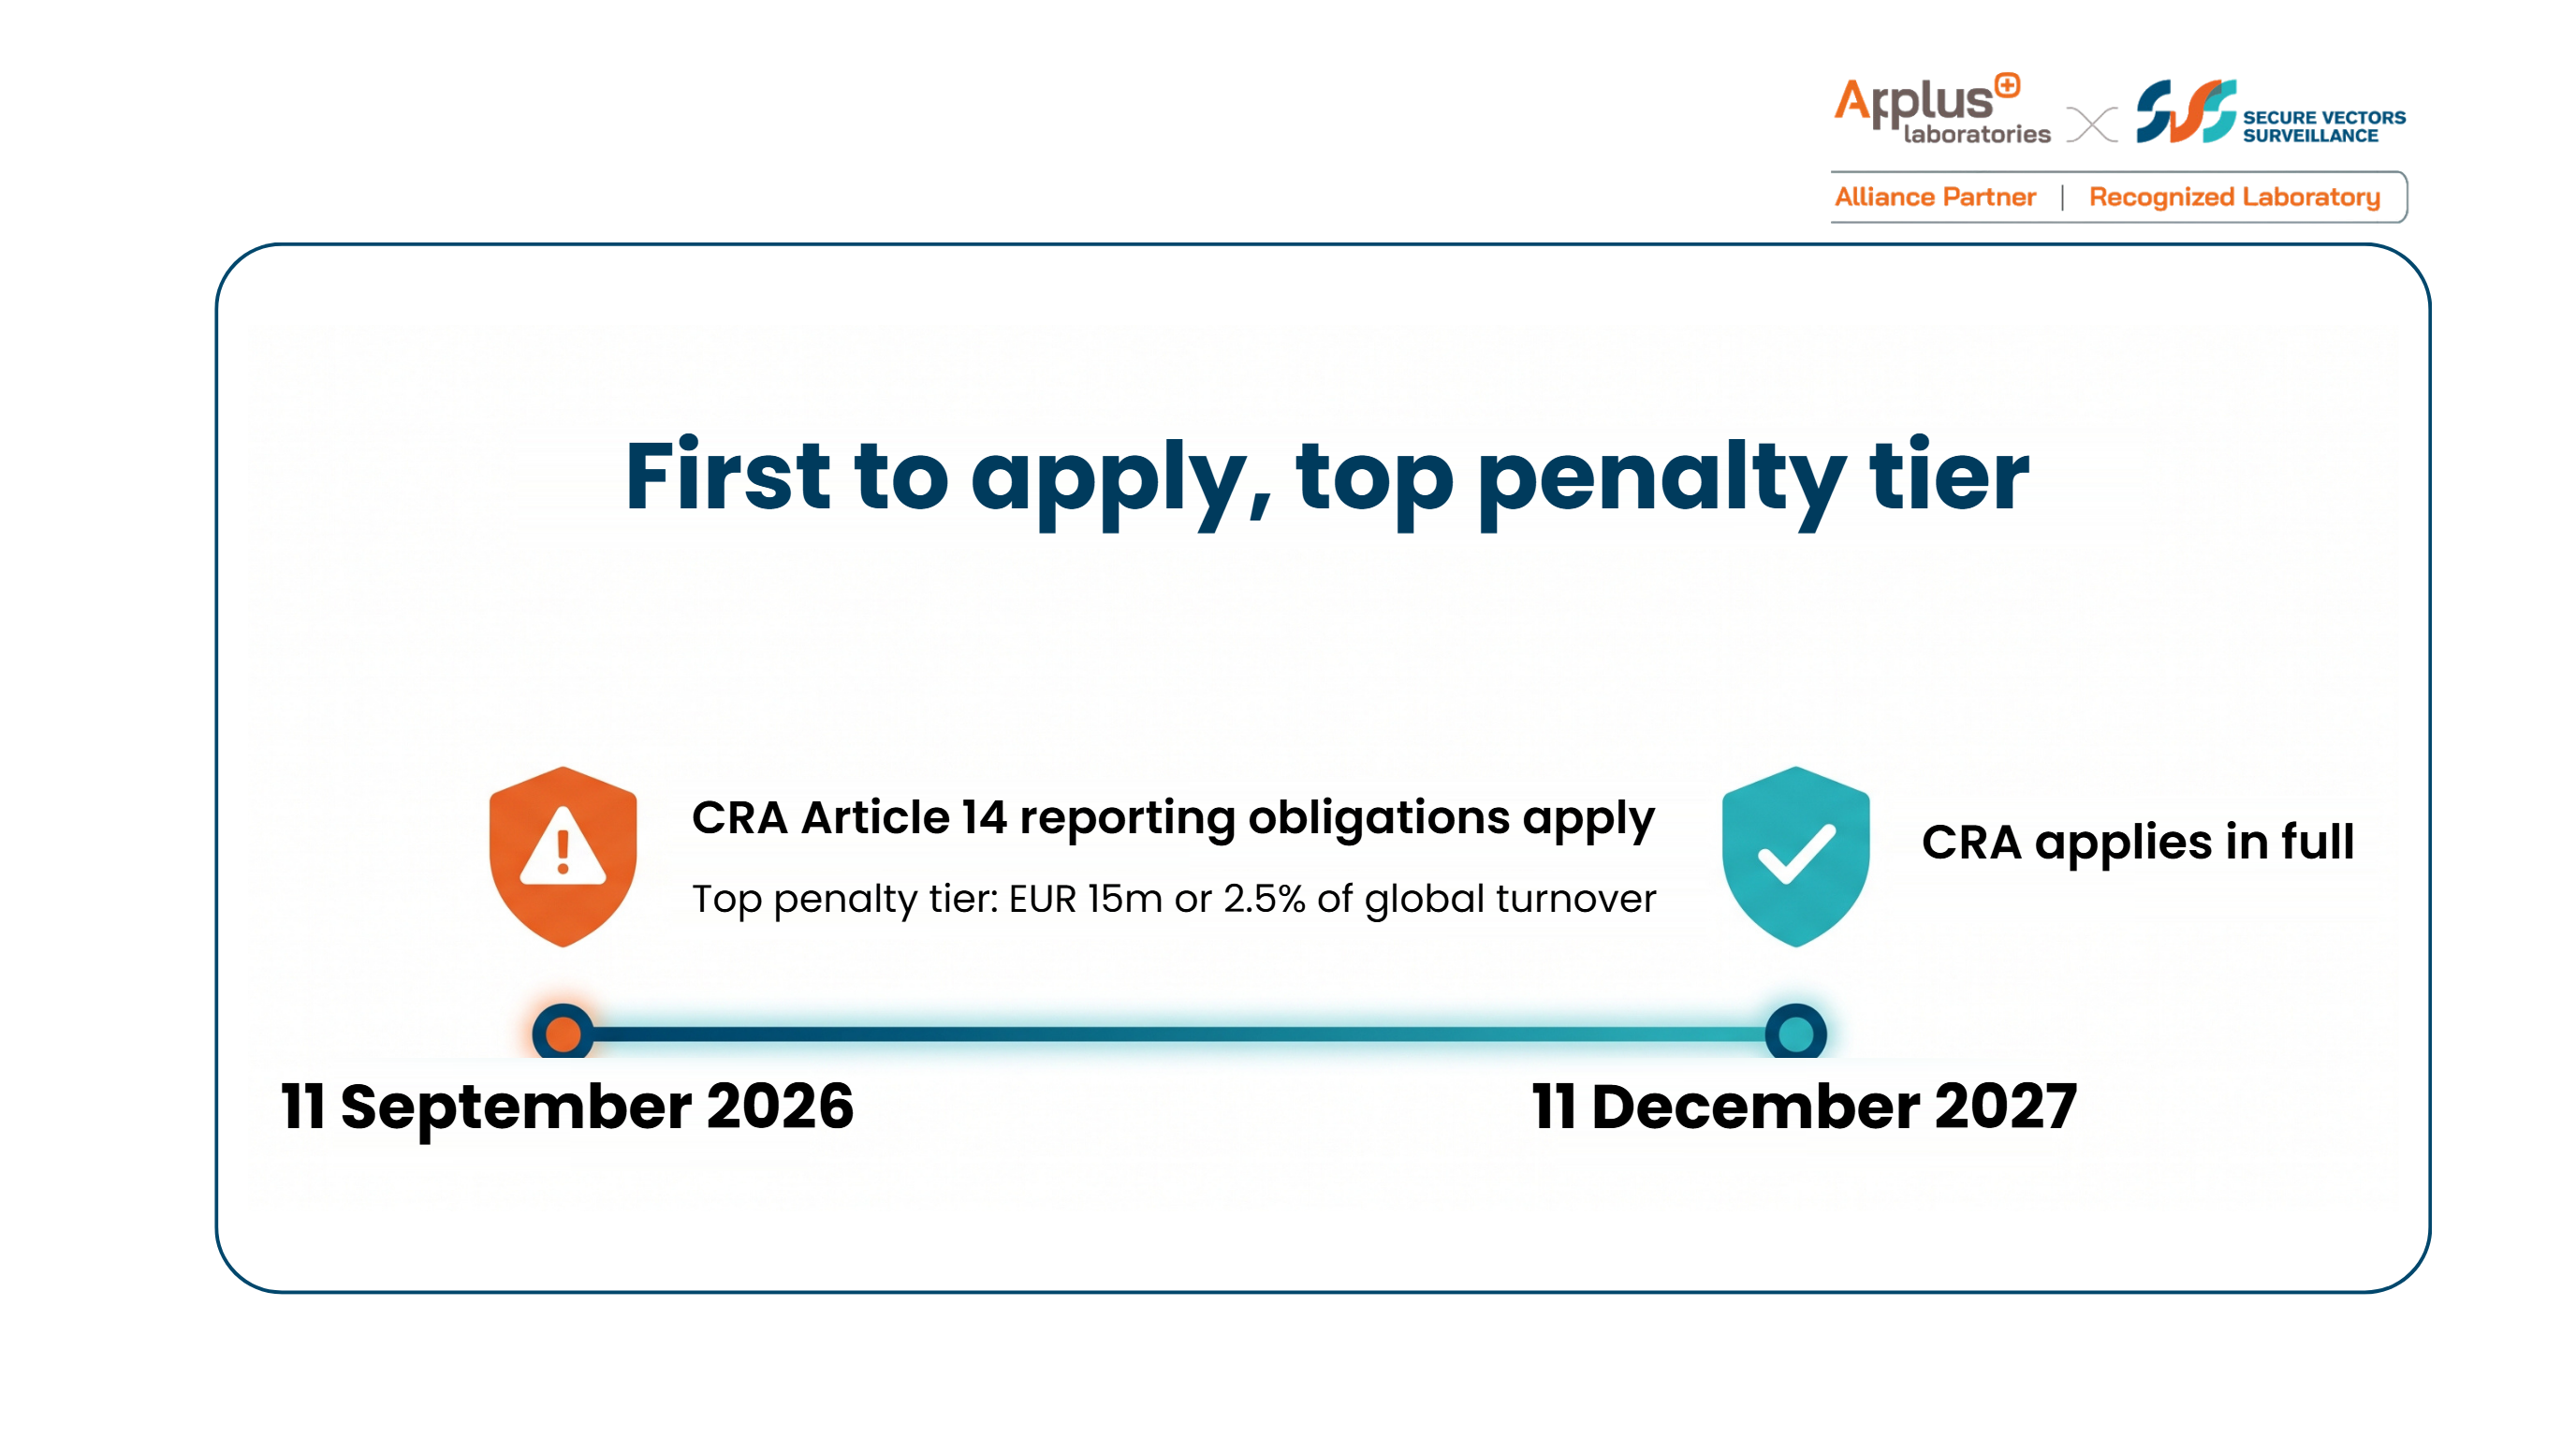
Part 1 | First to Apply, Top Penalty Tier: Inside CRA Article 14 Reporting Obligations

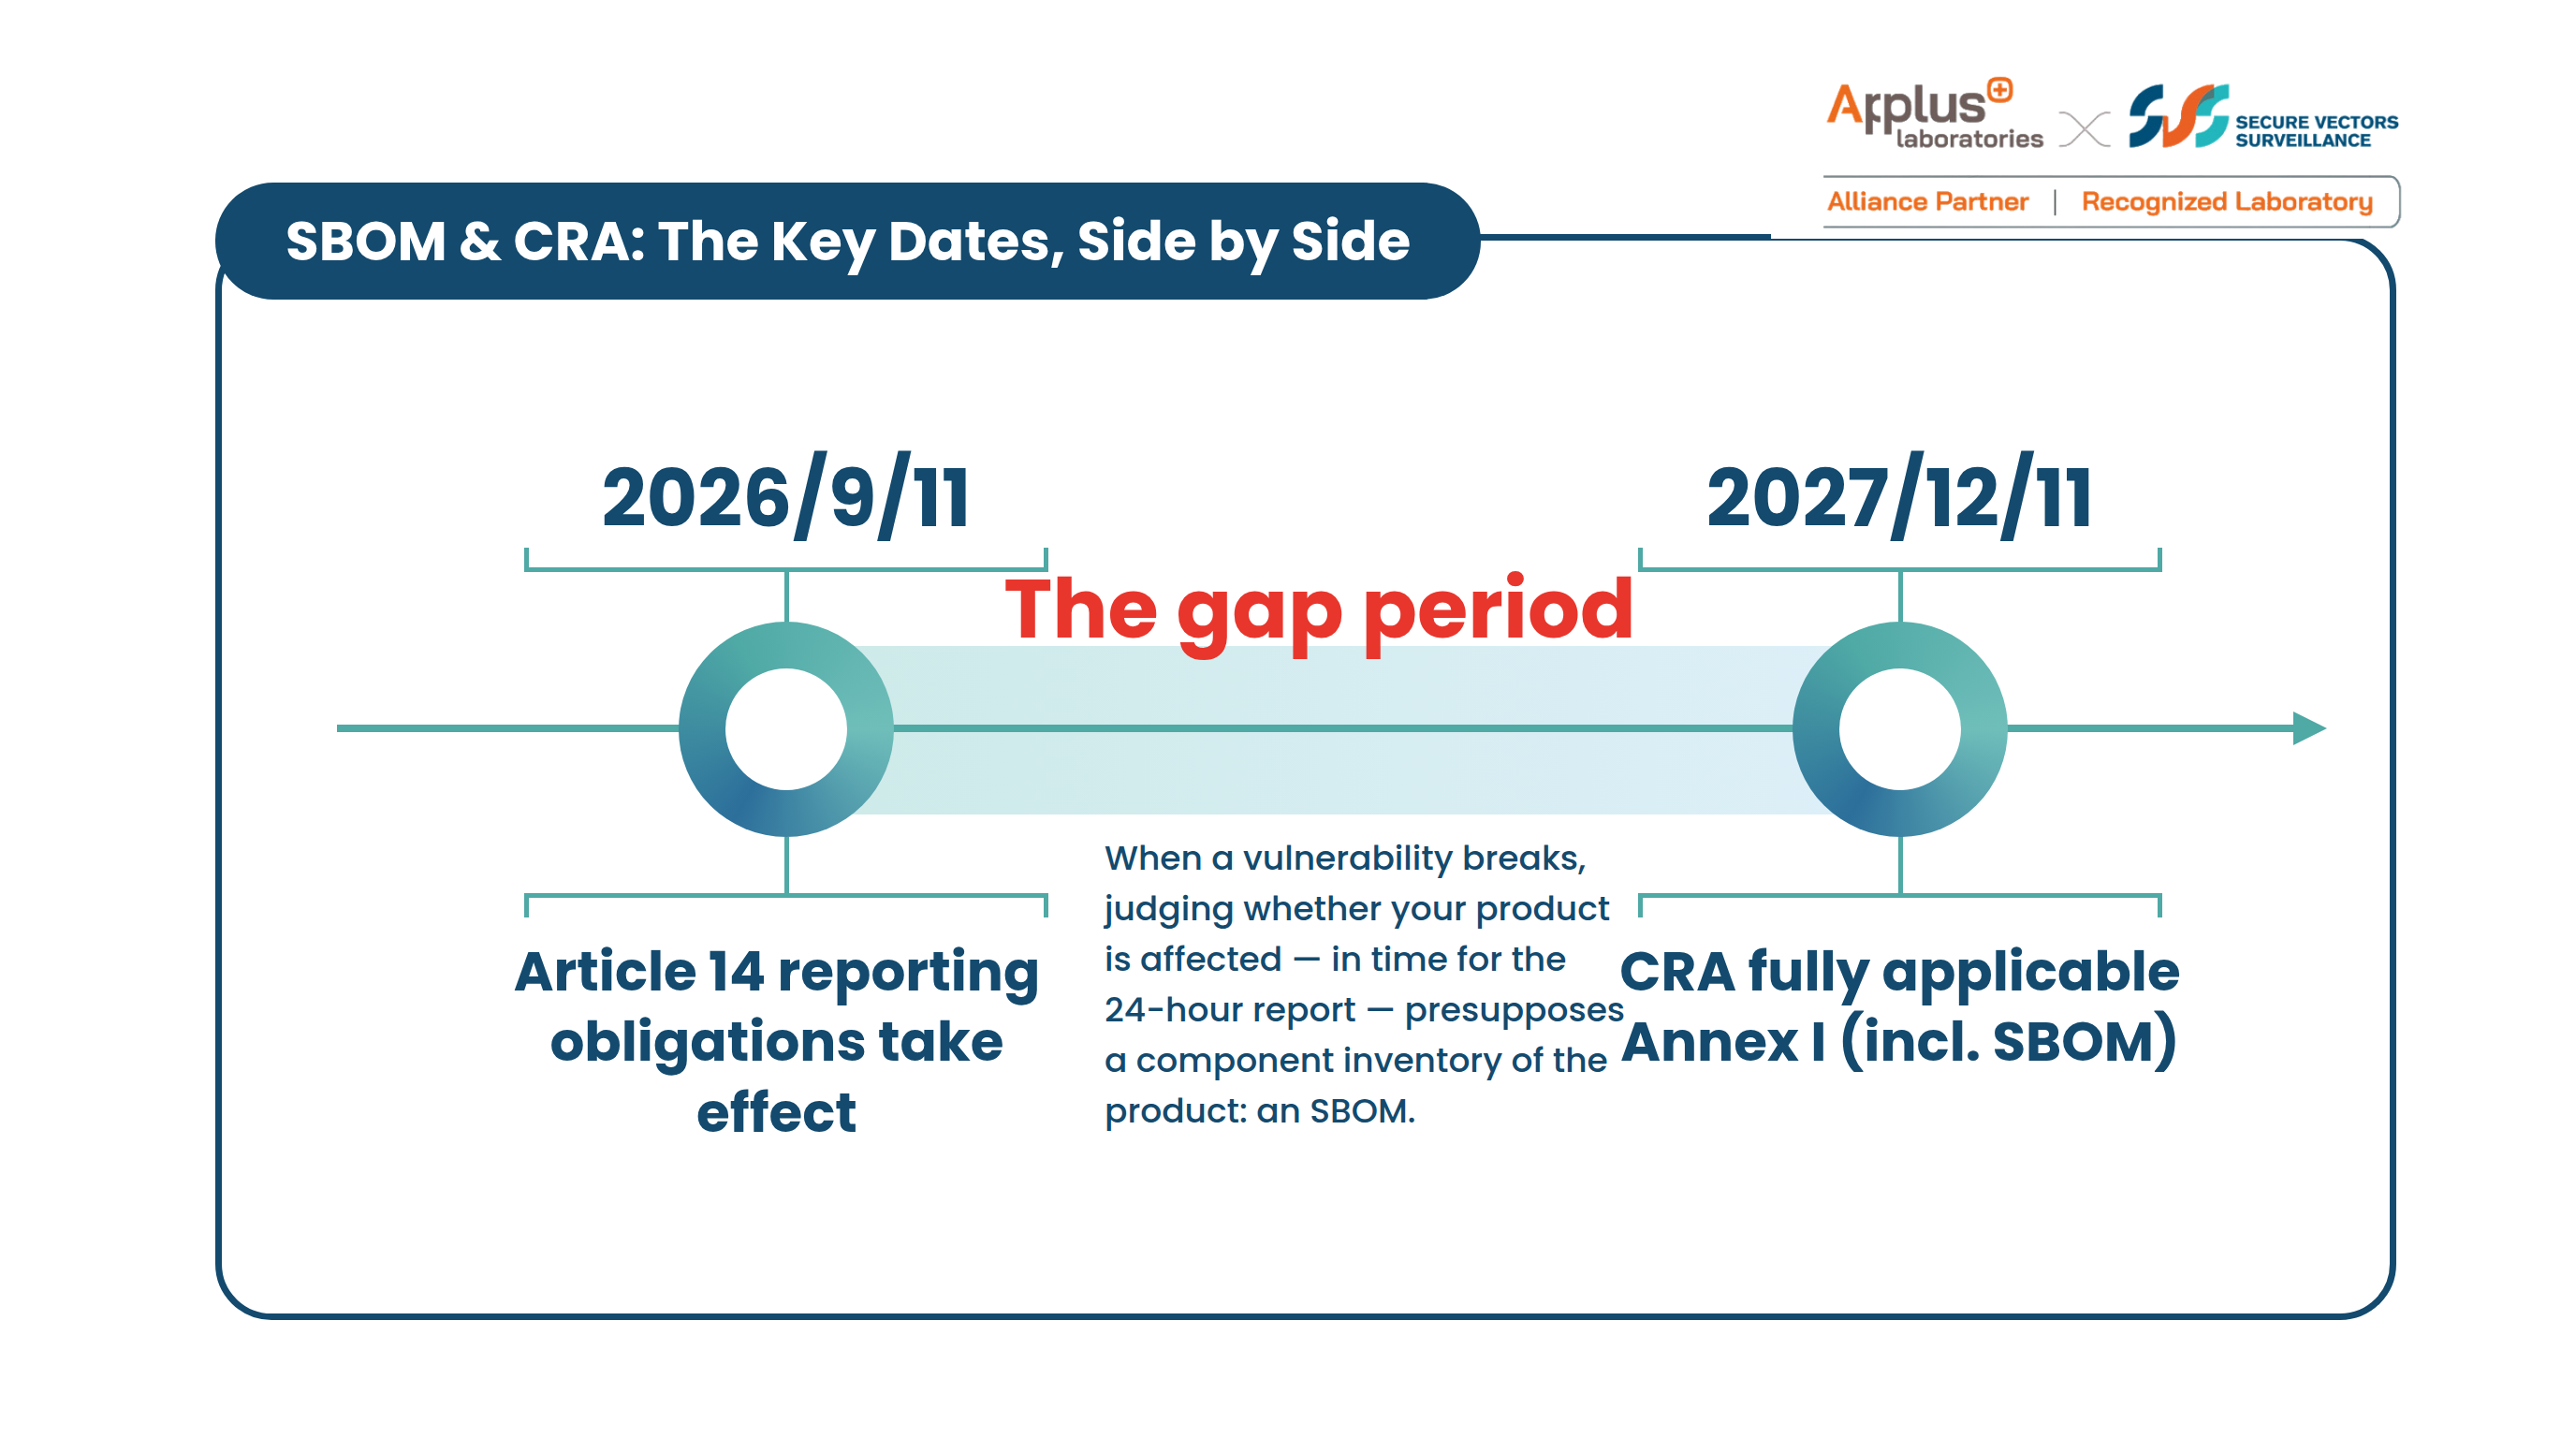
EU Cyber Resilience Act (CRA) Article 14 applies from 11 September 2026, well ahead of the 11 December 2027 general application date. This article breaks down the reporting duties for actively exploited vulnerabilities and severe incidents, the 24-hour / 72-hour / 14-day / one-month statutory deadlines, the top penalty tier, and the misreadings we see most often among manufacturers.

Read article →
https://securevectorlab.com/news/cra-article-14-reporting-obligations
Article cover
cra-product-scope
August 23, 2026

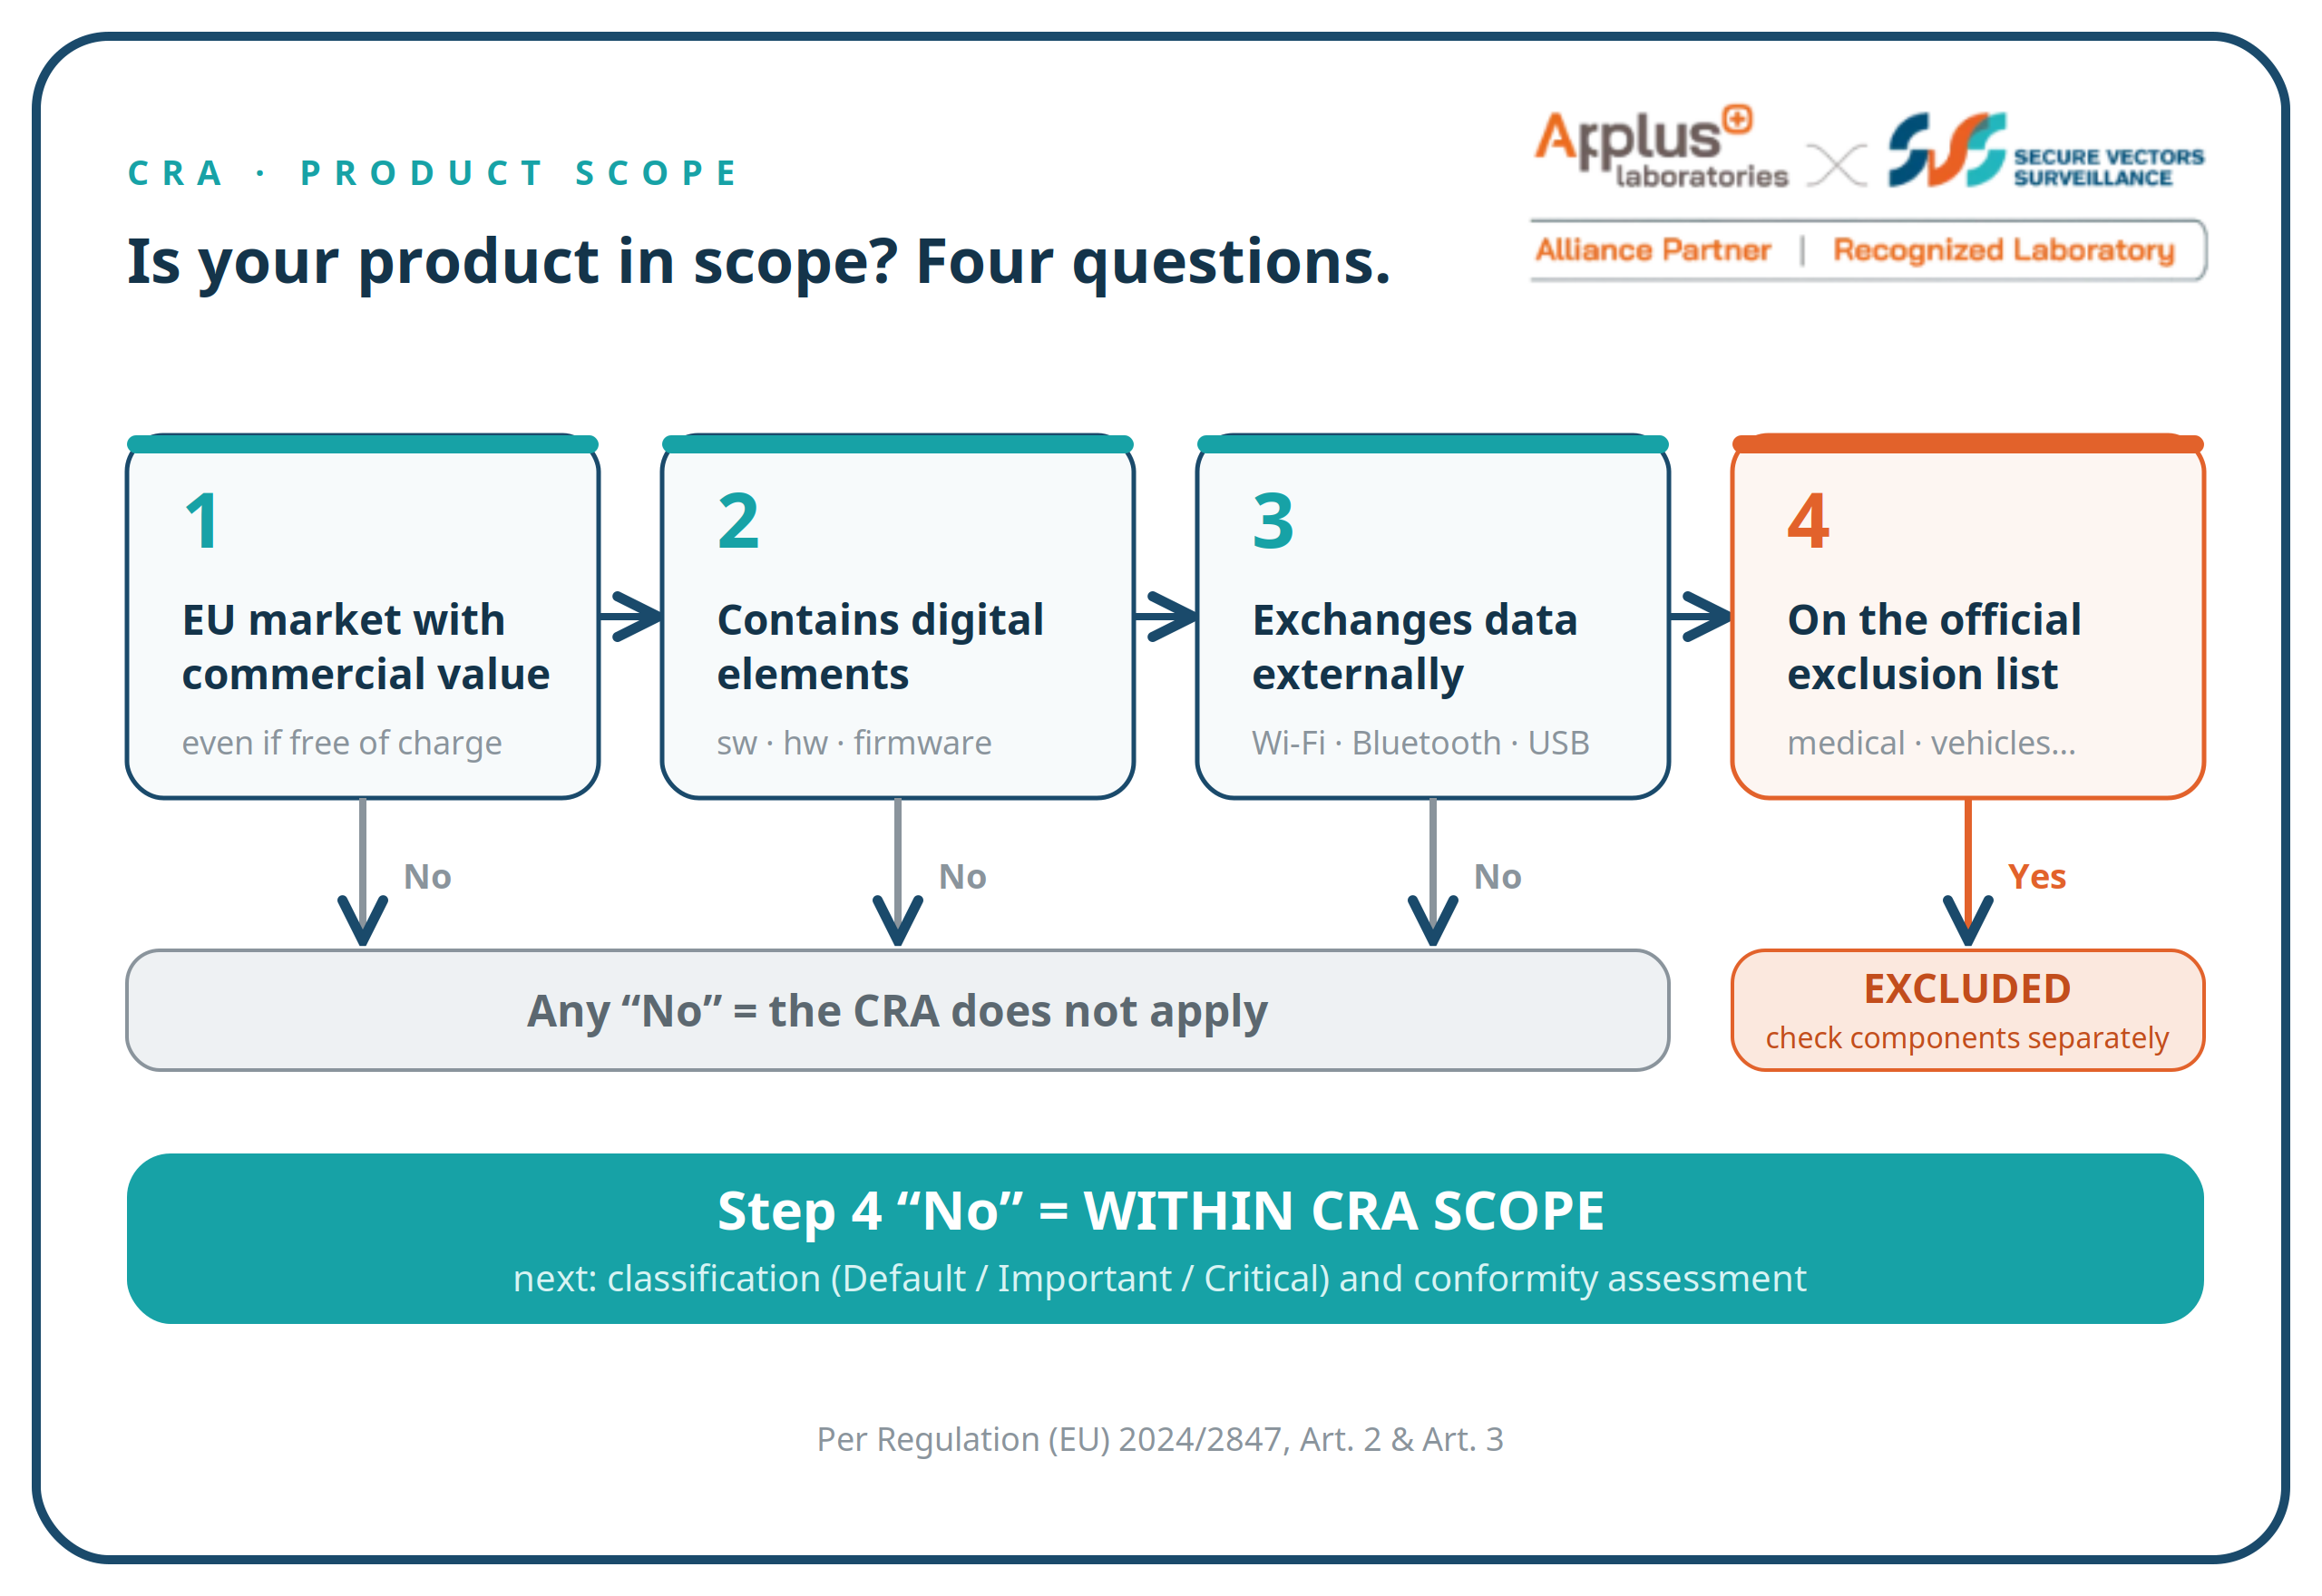
Selling into the EU — Does That Automatically Mean CRA? Start with Product Scope

Not every product sold into the EU falls under the Cyber Resilience Act (CRA). A four-step scope determination, with case studies on semiconductors, wireless communication modules, SaaS, and automotive T-Boxes — plus why “covered by the RED” doesn’t mean “excluded from the CRA.”

Read article →
https://securevectorlab.com/news/cra-product-scope
Article cover
cra-countdown-taiwan-ict-guide
July 29, 2026

CRA Countdown: Why Taiwan's ICT Makers Should Prepare Now

The EU Cyber Resilience Act is counting down, with fines up to 2.5% of global revenue. What EN 18031's three parts actually test, and why waiting until 2027 is too late.

Read article →
https://www.securevectors.com/cra-ict-deep-dive
Article cover
cio-taiwan-medical-device-security-lab
July 24, 2026

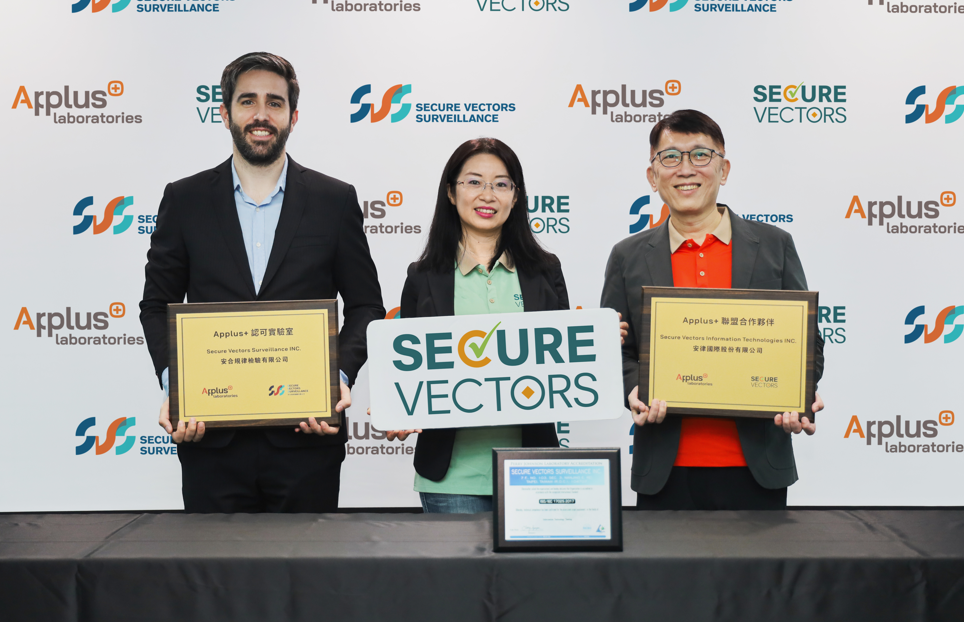
CIO Magazine: Connected Medical Device Security Levels Up — SV Surveillance Allies with Applus+ to Deliver One-Stop Local Compliance Support

As the US FDA, EU MDR, the CRA and Taiwan's TFDA keep raising cybersecurity requirements, SV Surveillance and Applus+ Laboratories build a Taiwan security lab to help medical device makers clear security verification.

Read article →
Article cover
mastercard-glb-12772
July 23, 2026

Mastercard GLB 12772 Alert | Refund & Chargeback Hits 5%, 72-Hour Investigation Required

Under Mastercard GLB 12772, a 5% refund/chargeback rate triggers a mandatory 72-hour investigation. See how Payment Facilitators should react.

Read article →
Article cover
credit-card-bin-compliance-guide-pci-dss-rules-for-8-digit-bin-storage-and-display
July 22, 2026

Credit Card BIN Compliance Guide | PCI DSS Rules for 8-Digit BIN Storage and Display

Master PCI DSS v4.0.1 rules for 6 and 8-digit BINs. Learn exact PAN truncation (storage) and masking (display) limits to secure your payment data.

Read article →
Article cover
fda-mdr-medical-device-cybersecurity-compliance
July 15, 2026

Medical Taiwan 2026 Exhibition Review : Secure Vectors Surveillance Forms Alliance with Applus+ Laboratories Creates a One-Stop Compliance Channel for FDA and MDR Medical Device Information Security

At Medical Taiwan 2026, Taiwanese device makers asked most about the MDR transition, FDA Section 524B, and the SVS-Applus+ route to FDA and MDR compliance.

Read article →
Article cover
ithome-cra-en18031-applus-alliance
July 15, 2026

iThome: CRA Countdown — Secure Vectors Surveillance Allies with Applus+ for One-Stop EN 18031 & CRA Testing in Taiwan

Secure Vectors Surveillance signs an alliance with Applus+ Laboratories, becoming a recognized security lab offering full EN 18031 testing and a one-stop CRA compliance path in Taiwan. (iThome coverage)

Read article →
Article cover
globalbio-mdr-fda-applus-alliance
July 8, 2026

Global Bio: MDR Transition Countdown — SV Surveillance and Applus+ Build a One-Stop MDR & FDA Security Compliance Channel for Taiwan's Medical Devices

On June 29, Secure Vectors Surveillance and Applus+ Laboratories formally signed their alliance: Taiwanese medical device makers can now complete the full path from QMS and security testing to EU Notified Body review locally.

Read article →
Article cover
cybersecurity-pren-40000-112026-hardware-devices-with-security-containers-hwsb-cra-compliance-guide
July 1, 2026

Cybersecurity | prEN 40000-11:2026: Hardware Devices with Security Containers (HWSB) · CRA Compliance Guide

prEN 40000-11:2026 gives Hardware Devices with a Security Box a harmonised route to EU CRA conformity: scope, the 18 requirement families, and evidence reuse.

Read article →
Article cover
who-protects-your-personal-privacy-understanding-the-iso-27701-privacy-information-management-system
June 10, 2026

Who Protects Your Personal Privacy? — Understanding the ISO 27701 Privacy Information Management System

What ISO 27701 (PIMS) covers, how it differs from ISO 27001, its link to GDPR compliance, and who needs certification.

Read article →
Article cover
a-guide-to-understanding-internal-auditors-for-system-certification
June 9, 2026

A Guide to Understanding Internal Auditors for System Certification

What internal auditors do in ISO management systems — why they're mandatory, how priorities shift across ISO standards, and the step-by-step audit process.

Read article →
Article cover
a-guide-to-understanding-iso-27001-information-security-management-in-the-medical-device-industry
June 4, 2026

A Guide to Understanding ISO 27001 Information Security Management in the Medical Device Industry

Why medical device makers need ISO 27001 — patient data sensitivity, IoMT attack surfaces, supply chain risk, and the 5-step certification process.

Read article →
Article cover
why-your-asv-scan-keeps-failing-cvss-thresholds-false-positives-what-to-fix
May 21, 2026

Why Your ASV Scan Keeps Failing: CVSS Thresholds, False Positives & What to Fix

Most ASV scan failures aren't real vulnerabilities — the CVSS 4.0 threshold, QSA-ready reporting, and the backporting trap explained.

Read article →
Article cover
understanding-the-iso-13485-medical-device-quality-management-system-in-one-article
May 11, 2026

Understanding the ISO 13485 Medical Device Quality Management System in One Article

What ISO 13485 is, why medical device companies need it, the 5-step certification process, and common misconceptions about the standard.

Read article →
Article cover
cybersecurity-countdown-to-the-eus-new-cra-regulations-mandatory-reporting-of-cybersecurity-incident
April 10, 2026

Cybersecurity | Countdown to the EU’s New CRA Regulations: Mandatory Reporting of Cybersecurity Incidents Starting in September 2026!

From September 2026 the EU Cyber Resilience Act makes Article 14 incident reporting mandatory. The two triggers, the reporting deadlines, and who to notify.

Read article →
Article cover
a-must-read-for-medical-device-manufacturers-when-cybersecurity-becomes-a-core-challenge-for-quality
March 18, 2026

A Must-Read for Medical Device Manufacturers: When Cybersecurity Becomes a Core Challenge for “Quality Leadership”

FDA guidance pushes medical device cybersecurity governance into the QMS — what QMSR harmonization and Section 524B mean for manufacturers.

Read article →
Article cover
our-alliance-partner-applus-laboratories-expands-emvco-accreditation-to-contactless-c-8-product-test
December 5, 2025

Our Alliance Partner Applus+ Laboratories Expands EMVCo Accreditation to Contactless (C-8) Product Testing

Applus+ Laboratories' Shanghai lab passed an EMVCo on-site audit, adding Contactless (C-8) testing - an accredited certification route for APAC terminal makers.

Read article →
Article cover
pci-approved-scanning-vendor-asv
October 21, 2025

📢 Secure Vectors Accredited as a PCI DSS Approved Scanning Vendor (ASV)

Secure Vectors is now a PCI SSC Approved Scanning Vendor, adding ASV to its QSA, 3DS and PIN Security accreditations. What ASV status demands, and why.

Read article →
Article cover
microsoft-issues-major-security-update
July 15, 2025

🔒 Microsoft Issues Major Security Update – 130 Vulnerabilities Patched!

Microsoft's July 2025 Patch Tuesday fixes 130 vulnerabilities including CVE-2025-49719 in SQL Server — what it means for PCI DSS environments.

Read article →
Article cover
red-compliance-deadline-august-1-2025-what-you-need-to-know
July 1, 2025

RED Compliance Deadline: August 1, 2025 – What You Need to Know

From August 1, 2025 all radio equipment sold in the EU must meet the RED cybersecurity requirements. Who is affected, EN 18031, and what to do if you miss it.

Read article →
Article cover
who-need-pci-dss-compliance
June 23, 2024

Who need PCI DSS Compliance?

Anyone storing, processing or transmitting cardholder data must meet PCI DSS. Here are the merchant and service provider levels and what each level submits.

Read article →
Article cover
what-is-your-saq-type
June 21, 2024

What is your SAQ Type?

There are 10 PCI DSS SAQ types. This guide compares SAQ A, A-EP and D for merchants and service providers, and walks through the five steps of self-assessment.

Read article →
Article cover
pci-dss-v4-0-12-4-2-2
October 19, 2023

How to meet the additional requirement for Service Provider only by PCI DSS v4.0 provision 12.4.2?

Service Providers must conduct quarterly inspections under PCI DSS v4.0 provision 12.4.2 — the 5 inspection items and how to comply.

Read article →
Article cover
gcp-news
August 15, 2023

[GCP] Be careful using GCP's CI/CD service Google Cloud Build!

Google Cloud Build may have a Bad.Build vulnerability allowing privilege escalation — what PCI DSS entities using GCP should check.

Read article →
Article cover
20230731001
July 31, 2023

【FortiOS】SSL-VPN Major Security Vulnerability (CVE-2023-27997) Have you fixed it?

A critical SSL-VPN flaw (CVE-2023-27997, CVSS 9.8) lets attackers run remote code on FortiOS, FortiOS-6K7K and FortiProxy. Check your version and patch.

Read article →
Article cover
immediate-response-required-windows-10-11-cve-2021-36934-security-vulnerabilities
October 13, 2021

Immediate Response Required: Windows 10/11 (CVE-2021-36934) Security Vulnerabilities

CVE-2021-36934 lets an ordinary Windows 10 or 11 user read system files and gain administrator rights. What it means for cardholder data, and how to fix it.

Read article →
Article cover
sequoia-cve-2021-33909-pci-dss
October 13, 2021

Sequoia Vulnerability (CVE-2021-33909), PCI DSS Experts advise

An out-of-bounds write flaw in the Linux kernel's seq_file — what it means for PCI DSS compliance and how to remediate.

Read article →
Article cover
pci-dss-compliance-process
October 13, 2021

PCI DSS Compliance Process and Requirements

An introduction to the PCI DSS compliance standards process, an explanation of PCI DSS levels of compliance and their required costs.

Read article →
Article cover
pci-3ds-assessment-and-certification
February 2, 2021

PCI 3DS Assessment and Certification

3DS 2.0 changes who must validate. This guide sets out which 3DSS, ACS, cloud and HSM providers need a PCI 3DS assessment, and the seven steps to certification.

Read article →

Related